MICROSOFT // SECURITY RESEARCH & AI ⌘K Executive Brief
Arjun Trivedi Executive Portrait
ARJUN TRIVEDI · @4R9UN · HYDERABAD, INDIA

Executive AI Security, Threat Research & Forward-Deployed AI Leader.

Senior Security Researcher at Microsoft (7+ years at Microsoft, 12+ years in Cybersecurity). Leads global Security Research & Applied Science teams—combining executive people leadership and organizational strategy with deep hands-on technical architecture to invent and ship breakthrough Agentic AI (Project Perception), RAG-grounded Security Copilot workflows (+35% accuracy), Official MCP Registry servers, Vibe Research Platforms, and multi-cloud detections protecting 1,000+ enterprises and 100M+ users.

EXECUTIVE MANDATE & VIBE RESEARCH PLATFORM Lead Security Researcher & Applied Scientist for Security Orgs

Pioneering Vibe Research Platforms for modern SOC & Threat Research organizations—combining Schema-Grounded MCP Servers (mcp-kql-server, fastmcp-threatintel), Multi-SIEM Autonomous Reasoning (ASRS), and Bounded Multi-Agent Harnesses (Assured-Arc) so security engineers move from raw telemetry to verified production detections in minutes.

EXECUTIVE RESEARCH MONOGRAPH · VOL. 2026

Arjun Trivedi — Grounded Agentic Defense & Enterprise AI Security

Over 12+ years in cybersecurity and 7+ years at Microsoft, Arjun Trivedi has bridged frontier AI research with high-stakes enterprise defense—leading global Security Research & Applied Science teams across Project Perception, Microsoft Security Copilot (+35% accuracy), adversarial AI Red Teaming, and Forward-Deployed Engineering for 50+ global enterprises.

Arjun Trivedi Portrait
AGENTIC AI ARCHITECT & SECURITY RESEARCH LEADER

Arjun Trivedi (@4R9UN)

Senior Security Researcher @ Microsoft · Security Research & Applied Science Leader · Creator of Official MCP Servers (mcp-kql-server, fastmcp-threatintel), ASRS & Assured-Arc.

# arjun_executive_profile.py — Verified Production Telemetry
class ArjunTrivediExecutiveLeader:
    role       = "Senior Security Researcher | Detection Eng & AI Security"
    org        = "Microsoft (7+ Yrs Microsoft | 12+ Yrs Cybersecurity)"
    leadership = "Global Security Research & Applied Science Team Leadership"
    pillars    = [
        "Agentic AI & MCP Architecture (Project Perception, Security Copilot +35%)",
        "AI Forward Deployed Engineering (50+ Enterprises, +20% CSAT, 1,000+ Adoptions)",
        "Applied ML & Detection Engineering (200+ KQL Rules -50% MTTR, ML -30% FP)"
    ]
CURSOR AGENT COMPOSER · VERIFIED OUTCOMES
Prompt: Summarize Arjun's category-of-one executive fit for Principal / Director / Head of AI Security & AI FDE roles.
Verified Output: Combines executive Security Research & Applied Science team leadership at Microsoft with deep hands-on solution creation across shipped MCP servers (PyPI v2.1.5 / v0.2.7), AI Red Teaming, and 50+ CISO/SOC enterprise FDE engagements.
Arjun Trivedi Portrait
PRODUCTION DEPLOYMENT // @4R9UN // MICROSOFT

Arjun Trivedi — AI Security & Agentic Systems.

12+ Years Cybersecurity · 7+ Years Microsoft · Leading Global Security Research & Applied Science Teams across Project Perception, Security Copilot (+35% Accuracy), Official MCP Servers, and 1,000+ Enterprise Deployments.

LEADERSHIP MANDATE Global Org Security Research & Applied Science
COPILOT RAG LIFT +35% Accuracy Context & Vector Grounding
SENTINEL ADOPTION 1,000+ Orgs Multi-Cloud Coverage Essentials
FDE ESCALATIONS 50+ Enterprises +20% Enterprise CSAT Improvement
EXECUTIVE AI SECURITY & FDE LEADERSHIP BRIEF

Enterprise-grade autonomous defense, built from field reality.

Arjun Trivedi (@4R9UN) leads global Security Research & Applied Science teams at Microsoft—combining executive team management and deep technical mastery to deliver Project Perception, Security Copilot (+35% accuracy), 50+ enterprise FDE engagements, and 1,000+ multi-cloud Sentinel deployments.

01 // EXECUTIVE VALUE PROPOSITION

Three Signature Market Pillars

Positioned for Principal, Director, Head of AI Security, Threat Research, and AI Forward Deployed Engineering (FDE) leadership mandates.

PILLAR 01 +35% Copilot Accuracy

Agentic AI & AI Security Architecture

  • Microsoft Project Perception: Contributed hunting & research agent capabilities applying organizational context, detection intelligence, and human-in-the-loop reasoning.
  • Microsoft Security Copilot: Improved threat summarization accuracy by 35% via RAG pipelines, vector grounding, and token optimization.
  • AI Red Teaming Lead: Hands-on adversarial testing for prompt injection, jailbreaks, unsafe tool invocation, authorization boundary failures, indirect instruction attacks, and excessive agency.
  • Official MCP Pioneer: Creator of MseeP-verified & Official MCP Registry servers (mcp-kql-server, fastmcp-threatintel), ASRS, and Assured-Arc.
PILLAR 02 1,000+ Enterprises · +20% CSAT

AI Forward Deployed Engineering (FDE) Leader

  • 50+ Enterprise Escalations Resolved: Embedded directly with global CISO & SOC teams to solve critical SIEM, XDR, and AI security blockers, lifting enterprise CSAT by 20%.
  • Multi-Cloud Attack Coverage Essentials: Co-created and shipped Microsoft Sentinel's flagship cross-cloud detection pack, adopted by 1,000+ enterprises across Azure, AWS, GCP, Okta, IBM & Oracle.
  • R&D-to-Production Flywheel: Directed rapid conversion of live customer telemetry and attack evidence into generally available capabilities across Sentinel, Defender XDR & Security Copilot.
PILLAR 03 200+ Detections · -50% MTTR

Security Research, Detection & Applied ML

  • Global Security Research & Applied Science Leadership: Combines executive team management, roadmap ownership, and mentorship (50+ engineers mentored) with hands-on invention across product engineering, data science & SOC operations.
  • 200+ Production KQL Rules: Engineered high-signal correlation analytics cutting enterprise incident response time (MTTR) by up to 50%.
  • Production ML Models (-30% FP): Built & validated Random Forest, Logistic Regression, Gradient Boosting, Isolation Forest & One-Class SVM models reducing false positives by 30%.
  • 20+ Python/Jupyter/MSTICPy Tools: Automated threat research workflows cutting analyst effort by up to 60%.
02 // CAREER TRAJECTORY (12+ YEARS CYBERSECURITY · 7+ YEARS MICROSOFT)

Complete Professional Experience

CURRENT ROLE · SECURITY RESEARCH & APPLIED SCIENCE LEADER Aug 2020 – Present · Hyderabad, India

Senior Security Researcher | Detection Engineering & AI Security — Microsoft

Global Research & Applied Science Lead +35% Copilot Lift 1,000+ Enterprises -50% MTTR

Agentic AI, Security Copilot & AI Red Teaming

  • Security Research & Applied Science Leadership: Leads multidisciplinary global detection engineering, security research, and applied science teams across product engineering, data science, operations, and enterprise customers—pairing executive people leadership with hands-on solution creation.
  • Microsoft Project Perception: Contributed research and hunting agent capabilities applying organizational context, detection intelligence, and evidence-grade reasoning with human oversight.
  • Microsoft Security Copilot (+35% Accuracy): Engineered retrieval-augmented threat summarization and optimized RAG context, token, and vector grounding to improve analyst accuracy by 35%.
  • AI Red Teaming: Executed adversarial evaluations of LLM & agentic security workflows covering prompt injection, jailbreaks, unsafe tool invocation, authorization boundary failures, indirect instruction attacks, and excessive agency.

Forward-Deployed Engineering, Applied ML & Multi-Cloud Detections

  • AI Forward Deployed Engineering (50+ Enterprises): Partnered directly with 50+ global enterprise customers on high-severity SIEM, XDR, and AI security escalations, lifting enterprise CSAT by 20%.
  • Multi Cloud Attack Coverage Essentials (1,000+ Orgs): Co-created and shipped Microsoft Sentinel's multi-cloud detection package spanning Azure, AWS, GCP, Okta, IBM & Oracle.
  • Applied ML (-30% False Positives): Built & validated production models using Random Forest, Logistic Regression, Gradient Boosting, Isolation Forest, and One-Class SVM.
  • 200+ KQL Rules & 20+ Automations: Cut enterprise MTTR by up to 50% across Sentinel/Defender XDR and built 20+ Python/Jupyter/MSTICPy tools reducing research effort by up to 60%.
PIONEER COHORT · MICROSOFT THREAT EXPERTS Mar 2019 – Aug 2020 · India

Cyber Threat Hunter | Microsoft Threat Experts — Microsoft

Pioneer Member Tier-1 Hunting SME Cross-Platform ML IOCs
  • Pioneer Service Launch: Founding member of Microsoft Threat Experts on-demand managed threat-hunting service protecting enterprise environments against human-operated adversaries and nation-state intrusions.
  • Tier-1 Hunting SME Lead: Led the Tier-1 hunting unit as Subject Matter Expert, triaging live enterprise intrusions and delivering executive-ready incident narratives.
  • ML & Telemetry Pipelines: Engineered automated ML and behavioral telemetry pipelines to surface novel IOCs across Windows, mobile, and cross-platform endpoints.
  • RE Quality Governance & Jupyter Automation: Established reverse-engineering quality controls for large contractor teams and authored reusable Jupyter threat-hunting notebooks.
MOBILE & ENTERPRISE REVERSE ENGINEERING Jun 2017 – Feb 2019 · India

Malware Analyst — Wipro

IDA Pro & Ghidra Android APK & Native RE Behavioral Sandboxes
  • Advanced Malware Reverse Engineering: Dissected complex Android APKs, DEX bytecode, and compiled native ARM/x86 libraries (.so) using IDA Pro and Ghidra.
  • PE & Non-PE Lab Architecture: Designed isolated behavioral detonation and memory-forensics sandboxes for packed Windows PE binaries and weaponized scripts.
  • Cross-Functional Threat Intelligence: Partnered across engineering, policy, and legal teams to neutralize active threat campaigns and authored technical white papers.
  • Analyst Mentorship: Trained and mentored junior malware analysts on unpacking, deobfuscation, and behavioral signature authoring.
GLOBAL ENDPOINT PROTECTION Sep 2014 – May 2017 · India

Threat Researcher — Sophos

100M+ Users Protected 150 Countries Zero-Day & Botnet RE
  • Static & Dynamic Reverse Engineering: Analyzed bots, worms, banking trojans, ransomware families, custom packers, and malicious office/PDF documents.
  • Planet-Scale Detection Engineering: Authored low-false-positive behavioral detection patterns and endpoint signatures shipped to 100M+ users across 150 countries.
FOUNDATIONAL DEFENSE R&D & TEACHING Early Career Foundations · India

Government Defense Malware-Detection R&D & Cybersecurity Instructor

Defense Malware R&D Exploit PoC Tooling Ethical Hacking Instructor
  • Confidential Government Defense Malware-Detection Project: Engineered Python malware-analysis automation, exploit PoC verification tooling, custom detection signatures, and air-gapped lab architectures.
  • Cybersecurity & Programming Instructor: Instructed engineers and students in Ethical Hacking, Offensive Security, C, C++, Java, PHP, and Android application development.
03 // SHIPPED ARTIFACTS (OFFICIAL MCP REGISTRY · PYPI · VERCEL · SENTINEL)

Six Flagship Production & Open-Source Systems

LIVE VERCEL DEMO · TYPESCRIPT Multi-SIEM Agentic SOC

ASRS: Autonomous Security Reasoning System

Multi-agent investigation control plane orchestrating specialized Triage, Deep Analysis, and Verdict agents across Microsoft Sentinel, Splunk, Elastic, and CrowdStrike with parallel hypothesis testing.

TypeScriptSentinelSplunkElasticCrowdStrike
OFFICIAL MCP REGISTRY · PyPI v2.1.5 ★ 24 Stars · MseeP Verified

MCP KQL Server (mcp-kql-server)

Production Model Context Protocol server powering schema-grounded NL2KQL execution against Azure Data Explorer & Microsoft Sentinel with local semantic memory, AST validation, and Azure Container Apps + Bicep + Managed Identity deployment.

PythonPyPI v2.1.5Official MCP RegistryAzure KustoBicep
★ 40 STARS · 14 FORKS · PyPI v0.2.7 MseeP Verified CTI MCP

FastMCP ThreatIntel (fastmcp-threatintel)

Multi-source Cyber Threat Intelligence MCP server correlating real-time IOCs across VirusTotal, AlienVault OTX, AbuseIPDB & IPinfo with automated MITRE ATT&CK mapping, STIX 2.1 objects, and interactive D3.js attribution graphs.

PythonPyPI v0.2.7MITRE ATT&CKSTIX 2.1D3.js
27+ SKILLS · MULTI-AGENT HARNESS Zero-Trust Agent Governance

Assured-Arc (Assured-Arc)

Portable, reversible GitHub Copilot multi-agent harness enforcing compact JSONL skill routing, disposable subagent isolation, strict MCP transport safety, prompt-injection containment, and bounded deterministic verification.

PowerShellPythonAgent EvaluationMCP Safety
1,000+ ENTERPRISE DEPLOYMENTS Microsoft Sentinel Content Hub

Multi Cloud Attack Coverage Essentials & KqlNexus

Co-created Microsoft Sentinel's cross-cloud detection & hunting notebook suite spanning Azure, AWS, GCP, Okta, IBM & Oracle—deployed by 1,000+ global enterprises to detect cross-identity and cloud control-plane attacks.

Microsoft SentinelKQLJupyterAWS / GCP / Azure / Okta
PRIVACY-FIRST AI & INFOSEC INDEX Local-First LLM Tooling

Prompt-Book & JupyterUniverse

Prompt-Book: Privacy-first, zero-cloud local workspace for organizing and red-teaming security LLM prompts. JupyterUniverse: Curated search index of offensive/defensive InfoSec Jupyter notebooks.

JavaScriptPythonLLM Prompt EngineeringJupyter
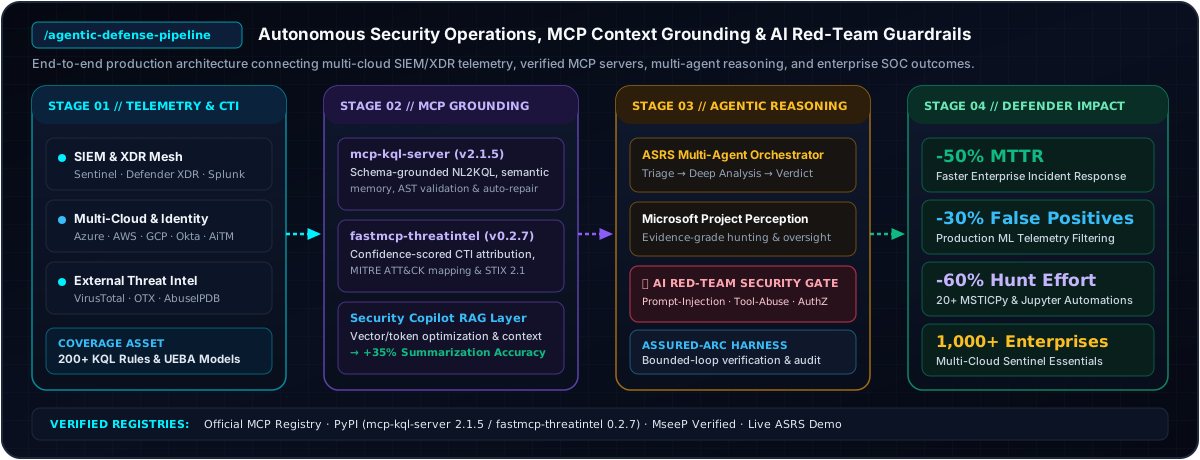
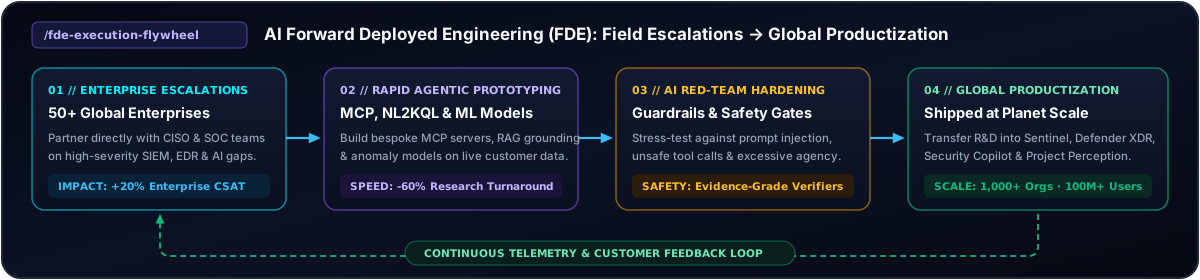
04 // PRODUCTION SYSTEM TOPOLOGY & EXECUTABLE GITHUB STACK

Agentic Security Pipeline & AI FDE Execution Loop

4-Stage Agentic Security Architecture Workflow Diagram
AI Forward Deployed Engineering Execution Flywheel
EXECUTABLE OPEN-SOURCE ARCHITECTURE

Run This Stack in 60 Seconds — Where Every Stage Lives on GitHub & How to Use It

Every stage in the architecture diagram above maps directly to shipped, open-source repositories under github.com/4R9UN, verified PyPI packages, and live sandboxes.

terminal — bash // Stage 01 & 02 PyPI Install
# 1. Install Official MCP Registry & MseeP-Verified Servers
pip install mcp-kql-server fastmcp-threatintel

# 2. Launch Schema-Grounded Sentinel NL2KQL or Multi-Source CTI MCP
python -m mcp_kql_server
fastmcp-threatintel
mcp-config.json — Claude / Copilot CLI / Cursor
{
  "mcpServers": {
    "kql-sentinel": {
      "command": "python",
      "args": ["-m", "mcp_kql_server"],
      "env": { "AZURE_CORE_ONLY_SHOW_ERRORS": "true" }
    },
    "threatintel-cti": {
      "command": "fastmcp-threatintel",
      "env": {
        "VIRUSTOTAL_API_KEY": "YOUR_VT_KEY",
        "OTX_API_KEY": "YOUR_OTX_KEY",
        "ABUSEIPDB_API_KEY": "YOUR_ABUSE_KEY"
      }
    }
  }
}
asrs-multi-siem — Sentinel · Splunk · Elastic · CrowdStrike
git clone https://github.com/4R9UN/ASRS-demo.git
cd ASRS-demo && npm install && npm run dev
powershell — Assured-Arc Copilot Security Harness
git clone https://github.com/4R9UN/Assured-Arc.git
pwsh -File .\Assured-Arc\scripts\install.ps1 -Profile full -Target both
STEP 01 // FIELD INTAKE

Enterprise Escalation & Gap Telemetry

Partner directly with CISO & SOC teams (50+ enterprises engaged) to capture high-severity multi-cloud, identity, or AI security gaps.

STEP 02 // VIBE RESEARCH

Rapid Agentic & NL2KQL Prototyping

Use mcp-kql-server + fastmcp-threatintel + MSTICPy to synthesize schema-pinned KQL and ML anomaly models (-60% research effort).

STEP 03 // AI RED-TEAM GATE

Adversarial Guardrails & FP Reduction

Validate agents against prompt injection & unsafe tool calls via Assured-Arc while ensemble ML cuts false positives by 30%.

STEP 04 // GLOBAL SHIP

Production Sentinel / Defender / Copilot

Ship verified analytics into Microsoft Sentinel Content Hub (1,000+ enterprises) & Security Copilot (+35% accuracy, -50% MTTR).

05 // ACADEMIC CREDENTIALS, CERTIFICATIONS & INDUSTRY RECOGNITION

Education, Certifications, Awards & Thought Leadership

ACADEMIC DEGREES

Education

2015 – 2017 M.Sc. in Information Technology

Amity University

2013 – 2015 B.Sc. in Computer Science (Information Technology)

K.R. Doshi Group of Computer Science College · M.K. Bhavnagar University

CERTIFICATIONS & AI TRAINING

Professional Development

SANS INSTITUTE SANS FOR578: Cyber Threat Intelligence

Advanced intrusion analysis, attribution, campaign tracking & executive CTI production.

MICROSOFT Microsoft SkillUp AI: Applied AI & Responsible AI Development

Enterprise LLM engineering, RAG grounding, safety guardrails & responsible AI governance.

APPIN TECHNOLOGIES Cyber Security & Ethical Hacking

Offensive security, exploit analysis, network defense & vulnerability assessment.

HONORS, MEDIA & COMMUNITY

Recognition & Leadership

MICROSOFT GLOBAL HACKATHON 🏆 Winner — Microsoft Global Hackathon 2023 (MSTICPy AI Assistant)

Also served as Hackathon Judge & Microsoft Security Hackathon 2025 participant.

PODCAST FEATURE 🎙 Featured Guest — AZ Security Podcast, Episode 27 ↗

Deep dive into MCP KQL Server, schema-grounded NL2KQL & AI-enabled SOC automation.

PUBLICATIONS & MENTORSHIP 📰 1,900+ Newsletter Subscribers & 15+ Technical Articles ↗

Published on Microsoft Tech Community & Substack; mentored 50+ security engineers globally.